CISA or CISM
CISA or CISM: which ISACA certification should you take?
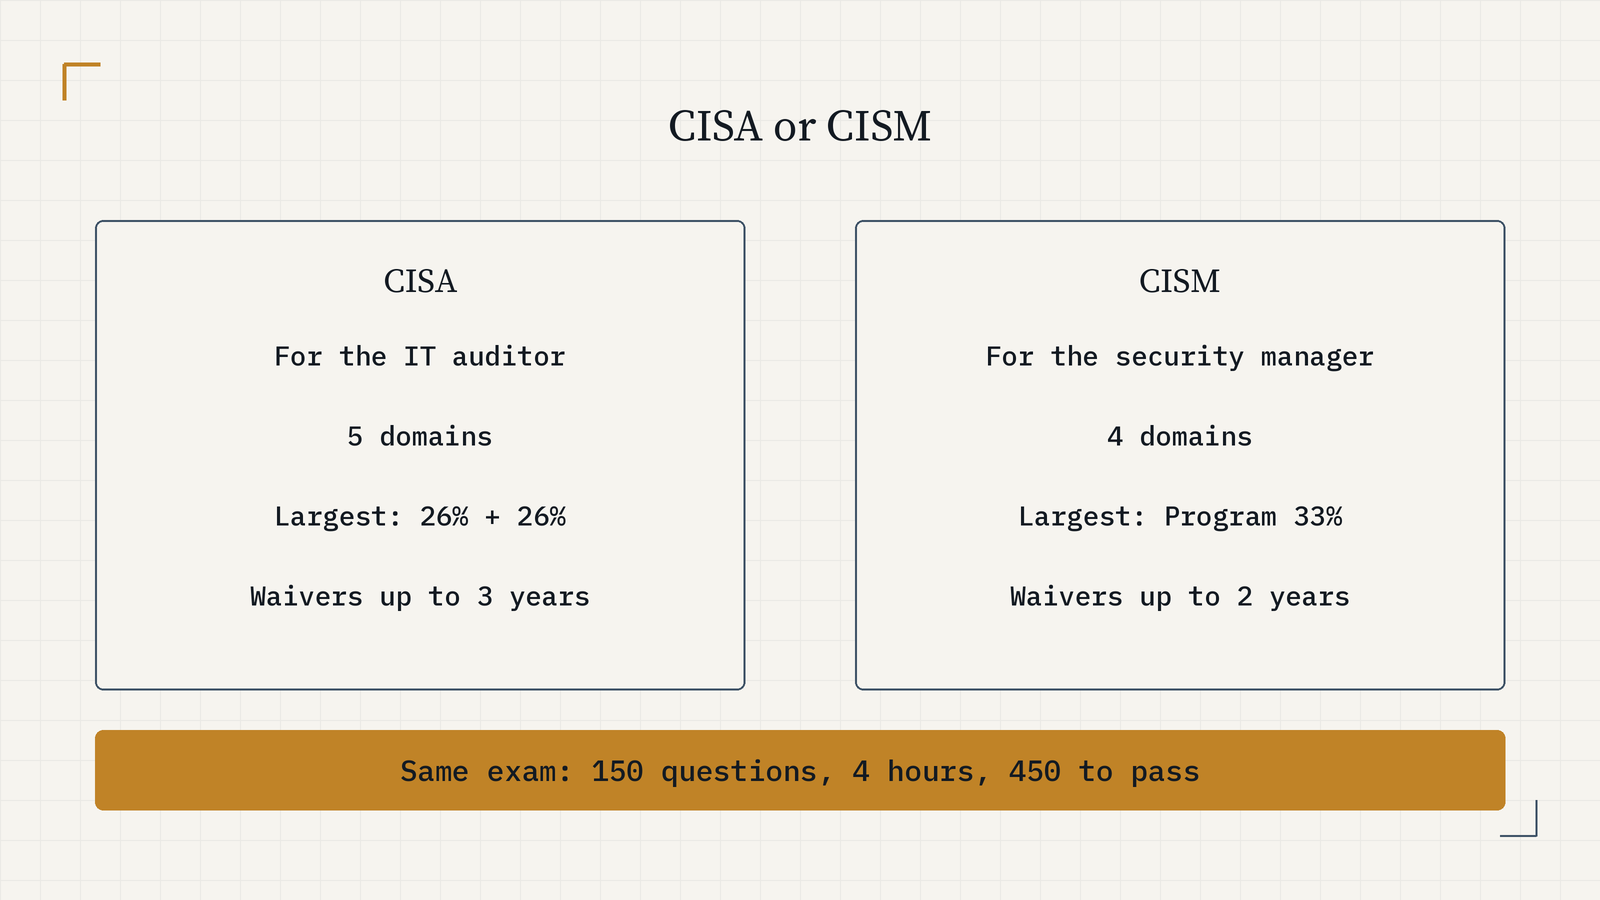
The CISA and the CISM come from the same board, use the same exam format and cost the same. What differs is the job. ISACA says the CISA validates "a modern IT auditor" and the CISM "a modern IT security manager". This page compares the two from ISACA's own documents, read on 2 October 2026, including the CISM outline change on 3 November 2026.
How do the CISA and the CISM compare?
| CISA | CISM | |
|---|---|---|
| ISACA says it validates | "a modern IT auditor" | "a modern IT security manager" |
| Domains | 5 | 4 |
| Largest domains | Operations and resilience; protection of information assets (26% each) | Information security program (33%) |
| Exam | 150 multiple-choice questions, 4 hours, 450 on a 200 to 800 scale, PSI test center or remote | |
| Fee | US$575 member, US$760 non-member; US$50 application fee after passing | |
| Experience | 5 years in IS audit, control, assurance or security; waivers up to 3 | 5 years in information security management, in at least 3 of 4 domains; waivers up to 2 |
| Upkeep | US$45 a year member, US$85 non-member; 20 CPE hours a year, 120 over three years | |
| Extra duty | Adhere to ISACA's IS auditing standards | None beyond the code of ethics and CPE policy |
Sources: ISACA's Exam Candidate Guide, version 1.26, the CISA and CISM pages, and the maintain pages for each. Our guides to the CISA exam outline and the CISM exam and its 2026 change have the detail.
What does each one test?
The CISA follows the outline ISACA made effective in August 2024: Information System Auditing Process (18%), Governance and Management of IT (18%), Information Systems Acquisition, Development, and Implementation (12%), Information Systems Operations and Business Resilience (26%), and Protection of Information Assets (26%). It asks whether you can plan and run an audit of IT and judge controls.
The CISM asks whether you can run security. Up to 2 November 2026 its weights are governance 17%, risk management 20%, program 33% and incident management 30%. From 3 November 2026 they become 18, 20, 33 and 29, and ISACA adds enterprise architecture and information security architecture as content areas.
Which suits which person?
Our reading of ISACA's descriptions: an internal or external IT auditor, or someone moving into assurance, fits the CISA. Someone who runs or wants to run a security function, owning policy, risk decisions and incident response, fits the CISM. A GRC analyst sits between them; if the work is mostly risk and controls, ISACA's CRISC, for "a modern risk management expert", is the third option. Our role-by-role certification guide puts all three side by side with the CISSP and others.
Role-to-credential matrix
Person,Current role,Main work today,Candidate credential,Board's audience statement fits (yes or no),Experience needed to certify,Experience held,Gap (years or hours),Can sit before the experience? ,Target exam date,Exam outline version and date,Book,Notes
Example: GRC analyst,GRC analyst,IT risk assessments and control testing,CRISC (ISACA),yes,3 years IT risk management and IS control (no waivers),2 years,1 year,Check with ISACA before booking,2027-03-01,Check isaca.org/credentialing/crisc,CRISC Exam Guide,
,,,,,,,,,,,,
,,,,,,,,,,,,
,,,,,,,,,,,,
"Experience rules read from each board's pages on 2 October 2026: ISACA (CISA 5 years, CISM 5 years, CRISC 3 years), ISC2 (CISSP and CCSP 5 years), PECB ISO Lead Implementer (5 years, 2 in the field, 300 project hours), GARP FRM (2 years full-time risk management). IAPP documents we read state no experience prerequisite for CIPP/E, CIPP/US, CIPM or CIPT. Template from credentialpress.com/guides/which-certification-for-which-role.",,,,,,,,,,,,
Can you sit before you have the experience?
Yes, for both. ISACA says you can take either exam before meeting the experience requirement, and you then have five years from passing to apply. The experience must fall within the ten years before you apply. CISA waivers go up to three years and CISM waivers up to two.
How should you prepare?
Split your hours by each outline's weights. Our CISA study plan does it for 50, 100 or 150 hours. For the CISM, check your exam date against 3 November 2026 first. The CISA study guide follows the August 2024 outline, and the CISM study guide follows the 2022 outline, for exams up to 2 November 2026.
What should you do this week?
Write down whether your work is mostly checking other people's controls or owning them. Checking points to the CISA; owning points to the CISM. Credential Press is independent of ISACA.
Frequently asked questions
What is the difference between the CISA and the CISM?
ISACA describes the CISA as validating the skills of a modern IT auditor, and the CISM as validating those of a modern IT security manager. The CISA tests auditing and assurance across five domains; the CISM tests security governance, risk, program and incident management across four.
Are the CISA and CISM exams the same format?
Yes. ISACA's Candidate Guide gives both as 150 multiple-choice questions in 4 hours, scored from 200 to 800 with 450 to pass, at a PSI test center or remotely proctored.
Which needs more experience, the CISA or the CISM?
Both need five years. The CISA's can be in IS audit, control, assurance or security, with waivers for up to three years; the CISM's must be in information security management, across at least three of its four domains, with waivers for up to two years.
Do the CISA and CISM cost the same?
Yes. The exam is US$575 for ISACA members and US$760 for non-members, the application fee after passing is US$50, and the annual maintenance fee is US$45 for members and US$85 for non-members, for each.
Can I hold both?
Yes, and ISACA lets a qualifying continuing education activity count toward more than one ISACA certification. Each certification still has its own annual maintenance fee, and from a third ISACA certification the fee drops to US$25 for members and US$50 for non-members.
CISA: test yourself in five minutes
Which books cover the CISA and the CISM?
Certified Information Systems Auditor. 12 chapters, 355 pages.
Certified Information Security Manager. 12 chapters, 342 pages.
Sources
Every fact above was read on ISACA's own pages on 2 October 2026. The "which suits which person" section is our reading.
- ISACA, Certification Exam Candidate Guide, version 1.26
- ISACA, CISA and CISA Exam Content Outline
- ISACA, CISM and CISM Exam Content Outline
- ISACA, Maintain CISA Certification and Maintain CISM Certification
Credential Press is not affiliated with, endorsed by or authorized by ISACA. Exam names and trademarks belong to their owners.