For teams
Which certification should an auditor, security manager, GRC analyst or privacy lead take?
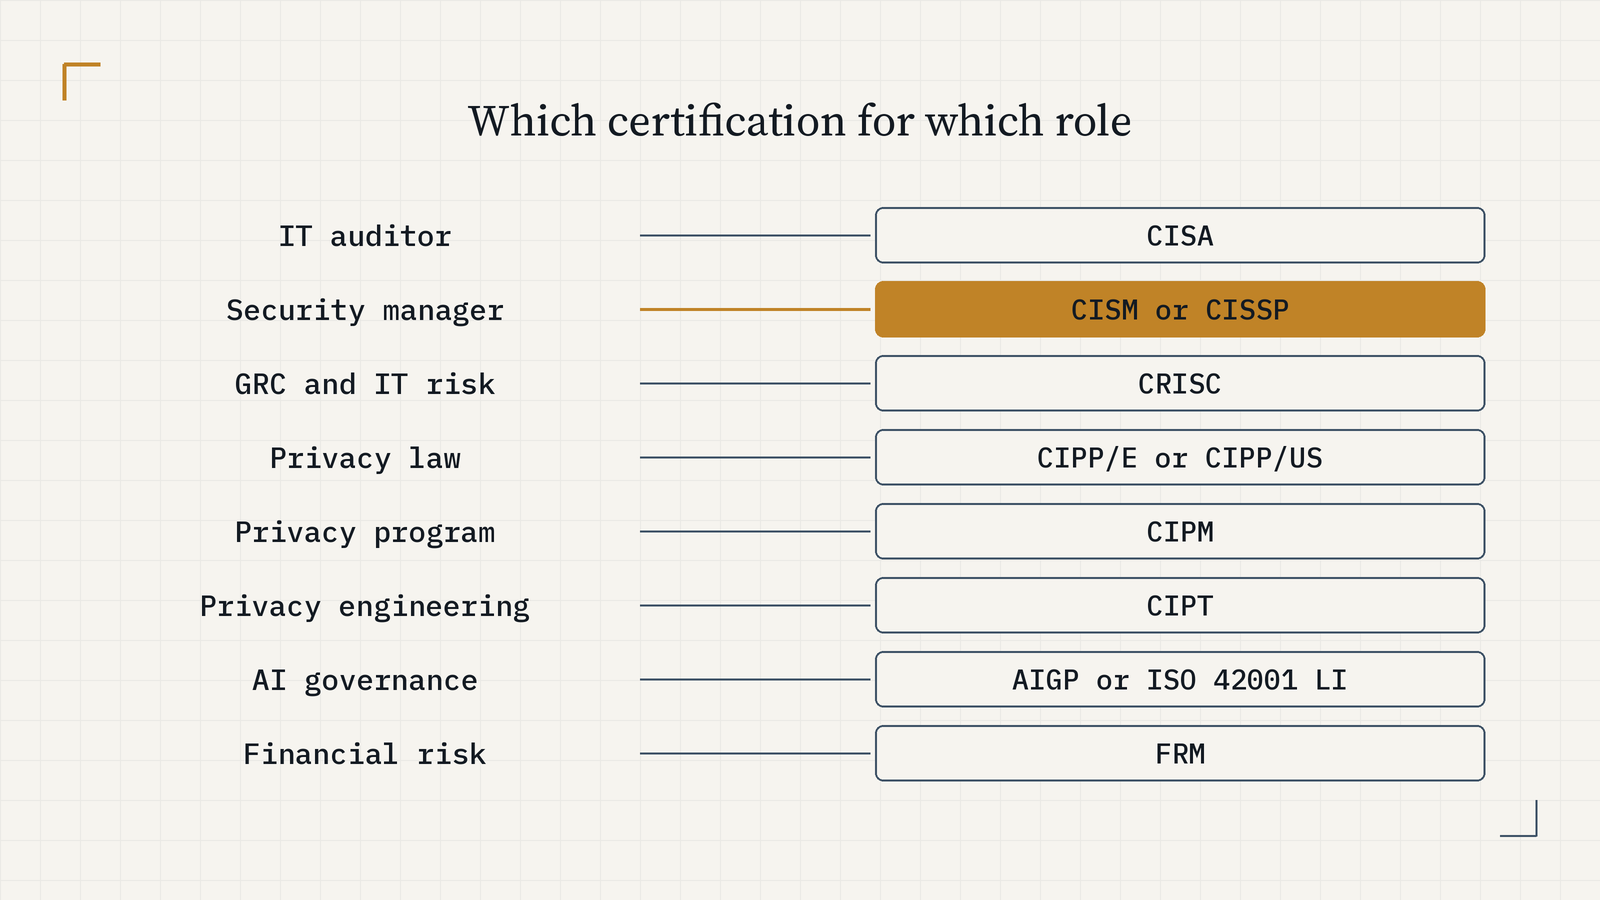
Every exam board says who its credential is for, and how much experience it takes to hold it. This page puts those statements side by side, role by role, in the boards' own words, so a manager can match people to certifications without relying on a training vendor's sales page.
The audience statements were read on each board's own pages on 2 October 2026: ISACA's credential pages, ISC2's certification pages, the IAPP's "Who should train?" sections, PECB's "Who should attend?" sections, and GARP's FRM FAQ.
Which credential fits which role?
| Role | Credential | What the board says | Experience to certify |
|---|---|---|---|
| IT auditor | CISA (ISACA) | Validates the skills of "a modern IT auditor" | 5 years in IS audit, control, assurance or security; waivers up to 3 |
| Security manager | CISM (ISACA) | Validates the skills of "a modern IT security manager" | 5 years in information security management; waivers up to 2 |
| IT risk and controls (GRC) | CRISC (ISACA) | Validates the skills of "a modern risk management expert" | 3 years in IT risk management and IS control; no waivers |
| Security practitioners, managers and executives | CISSP (ISC2) | "ideal for experienced security practitioners, managers and executives" | 5 years in two or more of the eight domains; one year can be waived |
| Cloud security | CCSP (ISC2) | For security leaders "responsible for applying best practices to cloud security architecture, design, operations and service orchestration" | 5 years |
| EU data protection | CIPP/E (IAPP) | "Data protection professionals whose work is within the scope of the General Data Protection Regulation" | None stated in the IAPP documents we read |
| US privacy | CIPP/US (IAPP) | "Everyone who needs in-depth knowledge of the U.S. privacy environment" | None stated |
| Privacy program | CIPM (IAPP) | "Professionals responsible for integrating privacy requirements into daily operations" | None stated |
| Privacy engineering | CIPT (IAPP) | Software developers, security professionals, data architects, privacy engineers, and network and cloud engineers | None stated |
| AI governance | AIGP (IAPP) | "Any professionals tasked with developing AI governance and risk management in their operations" | None stated |
| AI management system | ISO/IEC 42001 Lead Implementer (PECB) | "Professionals responsible for overseeing and managing AI projects", consultants, executives and managers | Lead Implementer: 5 years, 2 in AI, 300 hours of project activities |
| Business continuity | ISO 22301 Lead Implementer (PECB) | "Managers and consultants involved in business continuity" | Lead Implementer: 5 years, 2 in business continuity management, 300 hours |
| Financial risk | FRM (GARP) | Jobs including "risk analysis, model validation, trading, portfolio management, treasury, audit, consulting" | 2 years of full-time risk management work |
The experience rules come from ISACA's Exam Candidate Guide (version 1.26), ISC2's CISSP and CCSP pages, PECB's course pages, and GARP's FRM Exam Policies. For the IAPP, "none stated" means the handbook and FAQ we read give no education or experience prerequisite for sitting or holding these four credentials.
Role-to-credential matrix for your team
Person,Current role,Main work today,Candidate credential,Board's audience statement fits (yes or no),Experience needed to certify,Experience held,Gap (years or hours),Can sit before the experience? ,Target exam date,Exam outline version and date,Book,Notes
Example: GRC analyst,GRC analyst,IT risk assessments and control testing,CRISC (ISACA),yes,3 years IT risk management and IS control (no waivers),2 years,1 year,Check with ISACA before booking,2027-03-01,Check isaca.org/credentialing/crisc,CRISC Exam Guide,
,,,,,,,,,,,,
,,,,,,,,,,,,
,,,,,,,,,,,,
"Experience rules read from each board's pages on 2 October 2026: ISACA (CISA 5 years, CISM 5 years, CRISC 3 years), ISC2 (CISSP and CCSP 5 years), PECB ISO Lead Implementer (5 years, 2 in the field, 300 project hours), GARP FRM (2 years full-time risk management). IAPP documents we read state no experience prerequisite for CIPP/E, CIPP/US, CIPM or CIPT. Template from credentialpress.com/guides/which-certification-for-which-role.",,,,,,,,,,,,
CISM or CISSP for a security manager?
Both boards claim the role, so look at the outlines. The CISM has four domains, all at management level: governance, risk management, the security program, and incident management. The CISSP has eight, across security practice from risk management to software development security, and ISC2 lists 11 positions it suits, from Chief Information Security Officer to Network Architect. Both need five years of experience. One timing point for a team buying now: ISACA's new CISM outline applies from 3 November 2026, so material written to the 2022 outline, including our CISM study guide, fits exams sat up to 2 November 2026. Our guides to the CISM exam and its outline change and the CISSP exam format have the detail.
Which credential suits a GRC analyst?
By ISACA's own descriptions, the CRISC is the risk credential, the CISA the audit one and the CISM the security management one. The CRISC needs the least experience of the three, three years, and allows no waivers. A GRC analyst who mostly tests controls for audit may fit the CISA's description better. Read the outline of each against the person's actual work before booking; the CISA exam guide sets out its five domains and their weights.
Which privacy credential suits which person?
The IAPP splits privacy work three ways. The CIPP designations cover the law of a jurisdiction: CIPP/E for the GDPR and EU law, CIPP/US for US law. The CIPM covers running a privacy program. The CIPT covers building privacy into technology, and the IAPP names developers, data architects and engineers as its audience. A privacy team may need more than one, for example a DPO with the CIPP/E and the CIPM, and an engineer with the CIPT. The CIPP/E study guide and the CIPP/E exam outline are the usual starting points for an EU team.
AIGP or ISO 42001 Lead Implementer for an AI governance team?
They answer different questions. The IAPP's AIGP is for "any professionals tasked with developing AI governance and risk management", and covers AI laws, standards and frameworks across four domains. PECB's ISO/IEC 42001 Lead Implementer is built around implementing one standard's AI management system, from planning through to the certification audit. A team building a governance program from scratch may want the AIGP first; a team asked to implement ISO/IEC 42001 for certification will find the Lead Implementer the closer fit. See the AIGP blueprint by domain and the ISO 42001 Lead Implementer exam.
Can people sit the exam before they have the experience?
For most of these, yes. ISACA says candidates can take the CISA or CISM exam before meeting the experience requirement, and then have five years from passing to apply. ISC2 makes a CISSP passer without the experience an Associate of ISC2, with up to six years to earn it. GARP says FRM experience "can be accrued before or after you pass your Exams". PECB's Provisional Implementer credential needs no experience at all. So a junior team member can sit now and certify later, which spreads the cost over several budget years.
How should a manager choose?
Our suggestion, in order:
- Write down what each person does most weeks, then find the board statement in the table that describes it.
- Check the experience gap, and whether the person can sit before closing it.
- Check for an outline change, such as the CISM's on 3 November 2026, and make sure study material follows the current outline; the CCSP's changed on 1 August 2026.
- Price it with the team certification cost guide, which covers exam, maintenance and retake fees.
The matrix above has a column for each step. Our teams page lists the study guide for each credential.
What should you do this week?
Fill in the first four columns of the matrix for each person on the team, then check each candidate credential's audience statement on the board's own page before you commit budget. Credential Press is independent of every board named here.
Frequently asked questions
Which certification is best for an IT auditor?
ISACA describes the CISA as validating the skills of "a modern IT auditor". Certifying needs five years of IS audit, control, assurance or security experience, with waivers for up to three years, gained in the ten years before applying.
Should a security manager take the CISM or the CISSP?
Both boards name the role. ISACA says the CISM is for "a modern IT security manager", and ISC2 lists Security Manager among the positions the CISSP suits. The CISM has four management domains; the CISSP has eight domains across security practice. Both need five years of experience to certify.
Which certification suits a GRC or IT risk analyst?
ISACA describes the CRISC as for "a modern risk management expert", and it needs three years of IT risk management and IS control experience, with no waivers. For financial risk rather than IT risk, GARP's FRM is the closer fit.
Which certification should a privacy team take?
By the IAPP's own audience statements: CIPP/E or CIPP/US for the people who need the law, CIPM for those who integrate privacy into daily operations, and CIPT for engineers and architects who build privacy controls into technology.
Which certification is for AI governance?
The IAPP's AIGP is aimed at professionals developing AI governance and risk management. PECB's ISO/IEC 42001 Lead Implementer is aimed at people overseeing and managing AI projects who will implement an AI management system under the standard.
Can staff sit the exam before they have the experience?
For several credentials, yes. ISACA lets candidates sit the CISA and CISM first and apply within five years. ISC2 makes a CISSP passer without the experience an Associate with up to six years to earn it. GARP accepts FRM experience gained before or after the exams. PECB offers a Provisional Implementer credential that needs no experience.
Which books cover the two security manager credentials?
Certified Information Security Manager. 12 chapters, 342 pages.
Certified Information Systems Security Professional. 14 chapters, 396 pages.
Sources
Every statement above was read on the board's own pages on 2 October 2026.
- ISACA, CISA, CISM and CRISC pages, and the Exam Candidate Guide, version 1.26
- ISC2, CISSP and CCSP certification pages
- IAPP training pages: CIPP/E, CIPP/US, CIPM, CIPT, AIGP
- PECB course pages: ISO/IEC 42001 Lead Implementer and ISO 22301 Lead Implementer
- GARP, FRM FAQs and FRM Exam Policies
Credential Press is not affiliated with, endorsed by or authorized by ISACA, ISC2, IAPP, PECB or GARP. Exam names and trademarks belong to their owners.