For teams
What does NIS2 require of management bodies: approval, training, ten measures and 24-hour reporting?
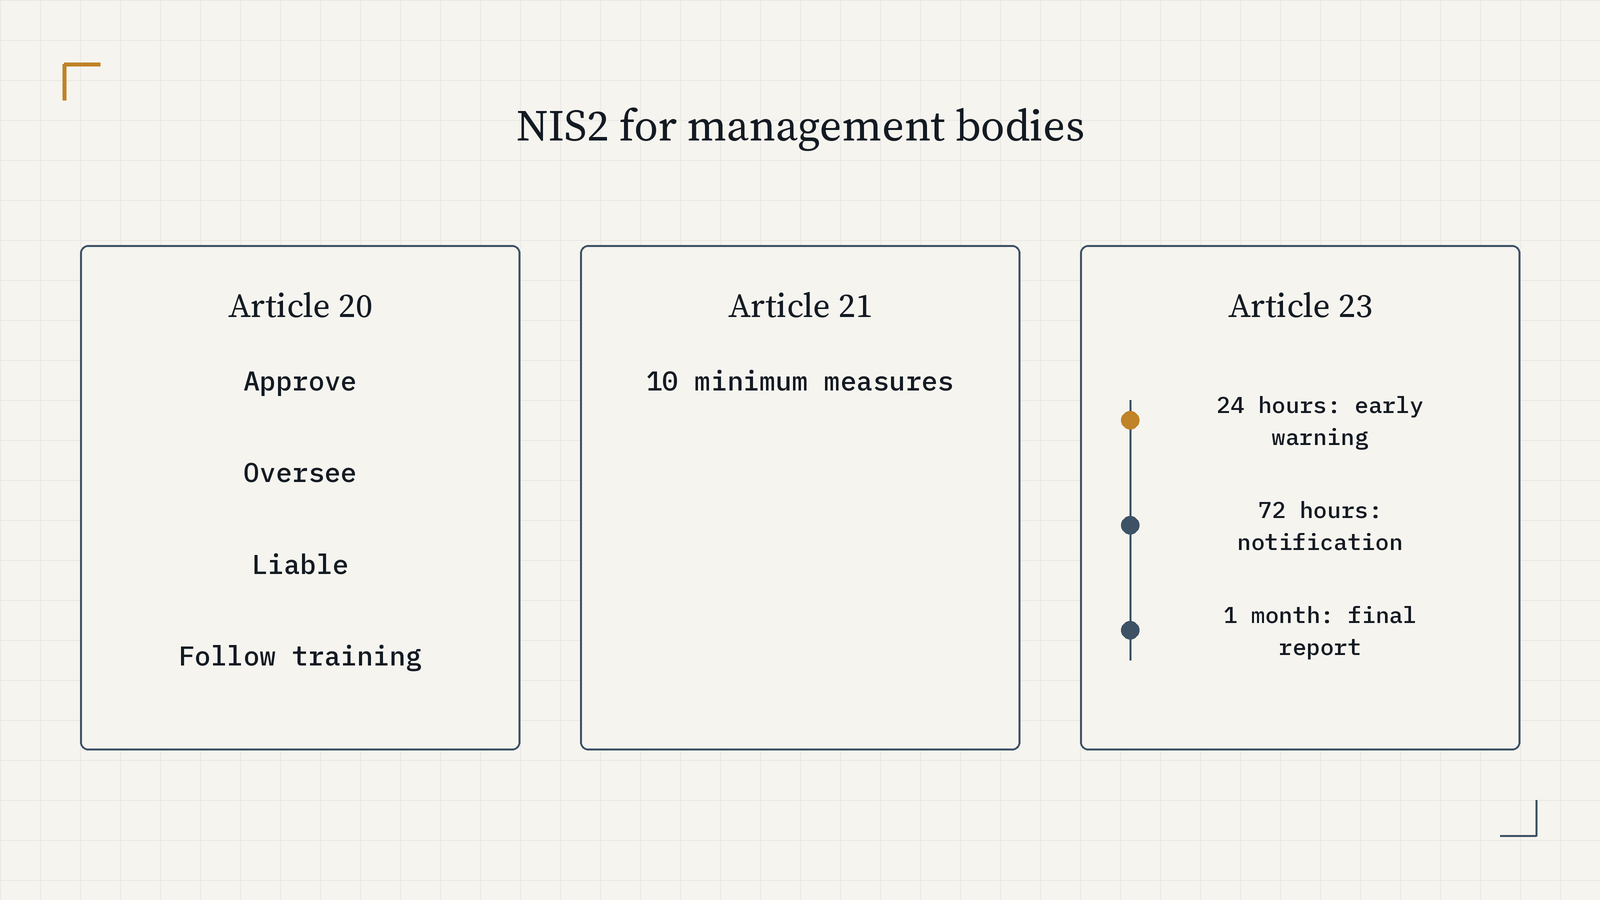
NIS2 puts cybersecurity on the board's agenda in writing. Article 20 makes management bodies approve the security measures, oversee them and answer for failures, and requires their members to follow training. Article 21 sets ten minimum measures, Article 23 sets reporting clocks of 24 hours, 72 hours and one month, and Article 34 sets the fines. This page quotes each from the Directive.
Every quotation is from Directive (EU) 2022/2555 (NIS2), OJ L 333, 27 December 2022, read on 2 October 2026; no amendment had been adopted by then. NIS2 is a directive, so the duties that bind an entity are in its country's transposing law. This is not legal advice.
What does Article 20 require of the management body?
Two things. Article 20(1) requires Member States to ensure that management bodies "approve the cybersecurity risk-management measures taken by those entities in order to comply with Article 21, oversee its implementation and can be held liable for infringements by the entities of that Article." Article 20(2) requires that their members "are required to follow training", and that entities are encouraged to offer similar training to employees "on a regular basis", so that they "gain sufficient knowledge and skills to enable them to identify risks and assess cybersecurity risk-management practices and their impact on the services provided by the entity."
So the board approves, oversees and is accountable, and it must be trained well enough to do that. Our guide to EU laws that require training sets NIS2 alongside DORA, the GDPR and the AI Act.
Which ten measures does Article 21 require?
Article 21(2) says the measures "shall be based on an all-hazards approach" and "shall include at least" these:
| Point | Measure |
|---|---|
| (a) | Policies on risk analysis and information system security |
| (b) | Incident handling |
| (c) | Business continuity, such as backup management and disaster recovery, and crisis management |
| (d) | Supply chain security, including relationships with direct suppliers and service providers |
| (e) | Security in acquisition, development and maintenance, including vulnerability handling and disclosure |
| (f) | Policies and procedures to assess the effectiveness of the measures |
| (g) | Basic cyber hygiene practices and cybersecurity training |
| (h) | Cryptography and, where appropriate, encryption |
| (i) | Human resources security, access control policies and asset management |
| (j) | Multi-factor or continuous authentication, and secured voice, video, text and emergency communications, where appropriate |
Article 21(1) makes the measures proportionate, taking into account the state of the art, relevant standards, cost, and the entity's exposure to risk and size. Article 21(4) requires an entity that finds it does not comply to take corrective measures "without undue delay".
NIS2 Article 21 checklist for the board
Article 21(2) measure,What NIS2 says (summary),Our policy or control,Owner,Evidence kept,Last reviewed,Approved by management body (Art. 20(1)),Notes
(a),Policies on risk analysis and information system security,,,,,,
(b),Incident handling,,,,,,
(c),"Business continuity, such as backup management and disaster recovery, and crisis management",,,,,,
(d),"Supply chain security, including security aspects of relationships with direct suppliers and service providers",,,,,,
(e),"Security in network and information systems acquisition, development and maintenance, including vulnerability handling and disclosure",,,,,,
(f),Policies and procedures to assess the effectiveness of cybersecurity risk-management measures,,,,,,
(g),Basic cyber hygiene practices and cybersecurity training,,,,,,
(h),"Policies and procedures on cryptography and, where appropriate, encryption",,,,,,
(i),"Human resources security, access control policies and asset management",,,,,,
(j),"Multi-factor or continuous authentication, secured voice, video and text communications and secured emergency communication systems, where appropriate",,,,,,
Article 20(2),Management body members follow training,,,,,,
Article 23(4)(a),Early warning within 24 hours of becoming aware of a significant incident,,,,,,
Article 23(4)(b),Incident notification within 72 hours,,,,,,
Article 23(4)(d),Final report within one month of the incident notification,,,,,,
"Directive (EU) 2022/2555, read 2 October 2026. NIS2 reaches you through national law, which may add to this list. Template from credentialpress.com/guides/nis2-management-body-duties. Not legal advice.",,,,,,,
What are the NIS2 reporting deadlines?
For a significant incident, one that has caused or could cause severe operational disruption or financial loss, or considerable damage to others, Article 23(4) sets four steps:
- An early warning "without undue delay and in any event within 24 hours of becoming aware of the significant incident", saying where applicable whether it is suspected to be malicious or could have cross-border impact.
- An incident notification within 72 hours, with an initial assessment of severity and impact and, where available, indicators of compromise.
- Intermediate reports on request of the CSIRT or competent authority.
- A final report "not later than one month after the submission of the incident notification", covering the incident, its likely root cause, mitigation and any cross-border impact.
Trust service providers notify within 24 hours instead of 72. The CSIRT or authority should respond to the early warning within 24 hours where possible. For AI systems, the EU AI Act has its own clocks; our guide to AI Act incident reporting covers them.
What are the NIS2 fines?
Article 34 sets floors for the maximum fines that national law must allow for infringing Article 21 or 23: for essential entities "a maximum of at least EUR 10 000 000 or of a maximum of at least 2 % of the total worldwide annual turnover", and for important entities at least EUR 7,000,000 or 1.4%, whichever is higher in each case. National law can set higher maximums.
Is NIS2 about to change?
On 2 October 2026, two Commission proposals to amend NIS2 were pending: the Digital Omnibus, COM(2025) 837, and COM(2026) 13. The second contains no change to Article 20. Neither had been adopted. Recheck before relying on this page in later months.
Who should run the program for the board?
A security lead who can translate the ten measures into policy, budget and evidence. ISACA's CISM is aimed at "a modern IT security manager", and its four domains cover governance, risk, program and incident management, which in our reading map closely to Articles 20, 21 and 23. The CISSP covers the technical breadth behind points (e), (h), (i) and (j). Our CISM or CISSP comparison helps choose, and the CISM exam study guide and CISSP study guide are on the teams page.
What should the board do this quarter?
Confirm under national law whether the entity is essential or important. Schedule the members' training and record it. Walk through the ten measures with the checklist above, assign an owner to each, and approve them on the record. Test the 24-hour early warning with a tabletop exercise. Credential Press is independent of the EU institutions.
Frequently asked questions
Are board members personally liable under NIS2?
Article 20(1) requires Member States to ensure that management bodies of essential and important entities approve the cybersecurity risk-management measures, oversee their implementation and can be held liable for infringements by the entity of Article 21. How that liability works is set by national law.
Does NIS2 require cybersecurity training for the board?
Yes. Article 20(2) requires Member States to ensure that members of the management bodies are required to follow training, and to encourage entities to offer similar training to employees on a regular basis.
What are the NIS2 incident reporting deadlines?
For a significant incident: an early warning within 24 hours of becoming aware of it, an incident notification within 72 hours, intermediate reports on request, and a final report no later than one month after the incident notification, under Article 23(4).
What security measures does NIS2 Article 21 require?
At least ten, from policies on risk analysis and incident handling through business continuity, supply chain security, vulnerability handling, cyber hygiene and training, cryptography, access control and asset management, to multi-factor authentication where appropriate.
What are the NIS2 fines?
For infringing Article 21 or 23, Member States must set maximum fines of at least EUR 10 million or 2% of worldwide turnover for essential entities, and at least EUR 7 million or 1.4% for important entities, whichever is higher.
Does NIS2 apply directly?
No. It is a directive, so it reaches entities through each Member State's transposing law, which had to apply from 18 October 2024 and may go further than the Directive.
Which books help the people who run the security program?
Certified Information Security Manager. 12 chapters, 342 pages.
Certified Information Systems Security Professional. 14 chapters, 396 pages.
Sources
Every quotation above was read from the Official Journal text on 2 October 2026 through the EU Publications Office.
Credential Press is independent of the EU institutions and of ISACA and ISC2. This is not legal advice.