ISO 27001
Who gets made the ISO 27001 Lead Implementer, and what are they expected to build?
The ISO 27001 Lead Implementer is usually not a job title anyone applies for. It is a role that lands on someone, often the security manager, sometimes the IT manager, quite often a consultant, on the day an organization decides it needs an information security management system that an auditor will accept. This guide is about that person: what they are expected to build, which events put the work on their desk, and when the PECB credential is the right way to prepare.
The facts here come from the standard's page at ISO, PECB's ISO/IEC 27001 Lead Implementer Candidate Handbook for the multiple-choice exam, version 1.5, PECB's course page, and the Official Journal texts of NIS2 and DORA.
What does an ISO 27001 Lead Implementer build?
An information security management system, or ISMS. ISO/IEC 27001:2022 is the third edition of the requirements for one, published in October 2022 by ISO and the IEC through their joint committee ISO/IEC JTC 1/SC 27, and since amended by ISO/IEC 27001:2022/Amd 1:2024. It does not tell you which firewall to buy. It tells an organization how to decide what to protect, assess the risks to it, choose controls, check that they work and keep improving, with records that prove each step happened.
In practice the implementer produces a small number of things that everything else hangs from. A written scope that says which parts of the organization, which sites and which systems are in. An information security policy that top management signs. A risk assessment method, the assessment itself and a risk treatment plan. A Statement of Applicability that lists every control in Annex A, says whether it applies and explains why. Then the operating rhythm that keeps the system alive: objectives, training, monitoring, internal audit, management review and corrective action.
The Statement of Applicability deserves its own sentence, because it is the document most people underestimate. Annex A groups its controls into four themes, organizational, people, physical and technological, with guidance on each in ISO/IEC 27002:2022, and the Statement of Applicability is where the implementer records the decision on every one of them. It is the document that ties the risk assessment to the controls, so a thin one points straight to a thin risk assessment.
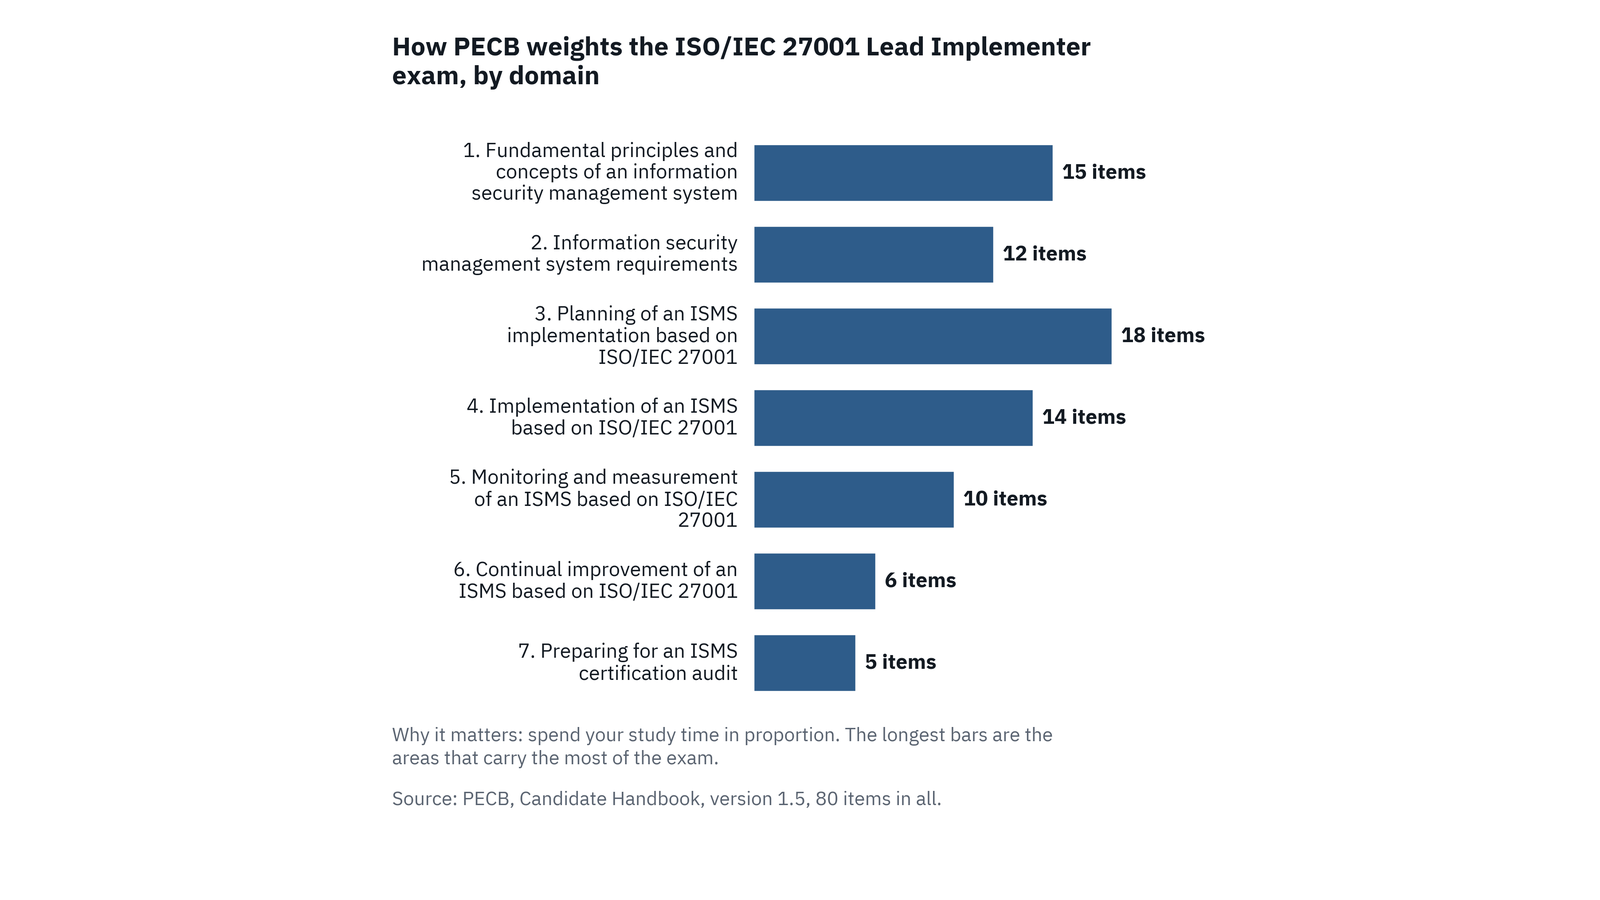
PECB weights its seven competency domains the way the job is weighted:
| Domain | Questions | Share |
|---|---|---|
| 1. Fundamental principles and concepts of an ISMS | 15 | 18.75% |
| 2. Information security management system requirements | 12 | 15% |
| 3. Planning of an ISMS implementation | 18 | 22.5% |
| 4. Implementation of an ISMS | 14 | 17.5% |
| 5. Monitoring and measurement of an ISMS | 10 | 12.5% |
| 6. Continual improvement of an ISMS | 6 | 7.5% |
| 7. Preparing for an ISMS certification audit | 5 | 6.25% |
The handbook also splits the paper by level of understanding: 43 questions test comprehension, application and analysis, and 37 test evaluation. Almost half the exam asks you to judge a situation, not to remember a clause.
Who gets sent on the course?
PECB's audience list for the five-day course names managers or consultants involved in implementing an ISMS, project managers, consultants and expert advisers who want to master ISMS implementation, people responsible for maintaining the ISMS's conformity, and members of the ISMS team. Put job titles on those descriptions and you get a familiar cast.
| Role | Why the work lands on them | What they need from the credential |
|---|---|---|
| Information security manager or CISO | They own the security program, so they own the management system that proves it | The structure an auditor expects, and the vocabulary to run it |
| IT manager in a smaller organization | There is no security team, and a customer has asked for a certificate | A safe order of work, so the project does not stall at the risk assessment |
| GRC, risk or compliance manager | They already run policies, risks and audits for other regimes | How ISO 27001 risk treatment and the Statement of Applicability work in detail |
| Consultant | Clients want someone who has done it before | A recognized credential and a method they can repeat |
| Project manager | The ISMS is run as a project with a deadline: the certification audit | Enough of the standard to plan the work in the right order |
| ISMS team member | They write the procedures and collect the evidence | Why each record matters, so the evidence holds up |
One role is missing on purpose. A penetration tester or security engineer will find the course readable and occasionally frustrating, because it spends little time on technical controls and a lot on decisions, records and governance. That is the point of the credential, and it is why the people who get the most from it are the ones who will have to make the system work as a whole.
When does the work land on your desk?
For most implementers there is a moment when the ISMS stops being a nice idea and acquires a deadline. These are the usual ones.
A customer asks for the certificate
Picture a sales team three weeks from closing a large contract. The customer's security questionnaire has a single blunt line: provide your ISO/IEC 27001 certificate, or explain how you meet an equivalent standard. Nobody can produce one. Someone is told to make it happen, and by the end of the week they are reading about the course.
The board decides to certify
Sometimes the decision comes from the top: a board wants the certificate as part of a growth plan, a funding round or a move into regulated markets. Certification is carried out by an accredited certification body, working to ISO/IEC 17021-1, in two stages: a documentation review and then an audit of the system in operation. The implementer's job is to have a system that passes both.
NIS2 or DORA reaches the organization
The NIS2 Directive, Directive (EU) 2022/2555, makes management bodies approve the cybersecurity risk-management measures, oversee them and answer for failures, and requires their members to follow training (Article 20). Article 21 sets ten minimum measures, from risk analysis and incident handling to supply chain security, cryptography and multi-factor authentication, and Article 23 sets reporting clocks of 24 hours, 72 hours and one month. For banks, insurers and other financial entities, DORA, Regulation (EU) 2022/2554, has applied since 17 January 2025: Article 5 makes the management body answerable for ICT risk, Article 6 requires an ICT risk management framework with an independent control function, and Article 13(6) makes security training compulsory for all staff. Neither law requires ISO 27001, but an ISMS is a natural place to hold the evidence both ask for. Our guides to NIS2 management body duties and DORA management body duties and training go article by article.
An incident, or a near miss
The least comfortable trigger is a breach, a ransomware scare or an auditor's finding that the organization cannot show who decided what about security. After that, leadership tends to want more than a fix. It wants a system that stops the same thing happening again, and somebody to build it.
What each trigger makes you produce
This is the table that saves the most time on a first ISMS project. Each trigger arrives with a different person asking, and each asks for different evidence first. Knowing which records come first saves weeks.
| Trigger | Who is asking | Evidence they want first | Where it lives in ISO 27001 |
|---|---|---|---|
| Customer questionnaire or customer audit | The customer's security or procurement team | Scope, policy, Statement of Applicability, latest internal audit | Clauses 4.3, 5.2, 6.1.3, 9.2 |
| Board decides to certify | The certification body, at stage 1 and stage 2 | Everything above, plus objectives, risk results, monitoring, management review, corrective action | Clauses 6.2, 8.2, 8.3, 9.1, 9.3, 10.2 |
| NIS2 applies | The national competent authority, and your own management body | Management approval of the measures, training records, the ten Article 21 measures with owners, an incident reporting procedure | Clauses 5.1, 6.1, 7.2, 7.3 and the Annex A controls you map each measure to |
| DORA applies | The financial supervisor | Management body approvals, the ICT risk framework, the independent control function, all-staff training | Clauses 5.1, 6.1, 9.2, 7.3, mapped to the DORA articles |
| Incident or audit finding | Leadership and, often, the insurer | Root cause, corrective action and proof it worked | Clauses 10.2, 9.1, 9.3 |
The same handful of records answers most of these. That is the quiet argument for building the ISMS properly once: the scope, the risk assessment, the Statement of Applicability and the internal audit cycle are reused every time somebody new asks a question. We have turned the table into a checklist you can copy below.
ISO 27001 trigger-to-evidence checklist
ISO 27001: trigger-to-evidence checklist
Use this when something lands on your desk and you need to know what the ISMS must be able to show. Clause numbers are ISO/IEC 27001:2022.
A customer security questionnaire or audit
- Scope of the ISMS, written down (clause 4.3)
- Information security policy, approved by top management (clause 5.2)
- Risk assessment results and risk treatment plan (clauses 6.1.2, 6.1.3, 8.2, 8.3)
- Statement of Applicability, with the reason each Annex A control is in or out (clause 6.1.3)
- Latest internal audit report (clause 9.2)
A certification decision by the board
- Every item above, plus information security objectives and plans to meet them (clause 6.2)
- Evidence of competence and awareness for people doing the work (clauses 7.2, 7.3)
- Monitoring and measurement results (clause 9.1)
- Management review minutes (clause 9.3)
- Nonconformities and the corrective action taken (clause 10.2)
NIS2 applies to the organization (Directive (EU) 2022/2555)
- Management body approval of the cybersecurity risk-management measures (Article 20)
- Training records for members of the management body (Article 20)
- The ten minimum measures of Article 21(2), each mapped to a policy, a control and an owner
- Incident reporting procedure that can meet 24 hours, 72 hours and one month (Article 23)
DORA applies to the organization (Regulation (EU) 2022/2554)
- Management body approvals for ICT risk (Article 5)
- ICT risk management framework and its independent control function (Article 6)
- Security awareness training for all staff (Article 13(6))
Before you call yourself ready
- Each item has an owner, a date and a place where the evidence lives
- Someone other than the author has checked the evidence against the clause
Where does the credential apply?
ISO/IEC 27001 is an international standard, and the certificate is recognized wherever accredited certification bodies operate. PECB runs the exam worldwide, remotely through the PECB Exams application with an online invigilator, or on paper through the partner that ran your course. For online multiple-choice exams, PECB says candidates receive their results instantly, and candidates sitting a Lead exam in a language that is not their own can ask for 30 extra minutes.
What varies by country is the regulation around the standard. Inside the EU, NIS2 and DORA give the work a legal edge for the organizations they cover. Outside it, the pressure usually comes from customers, contracts and tenders rather than from a regulator.
What the credential is not
It is not your organization's certificate. The Lead Implementer is a personal credential. The certificate on the reception wall comes from a certification body after an audit, and holding the first does not give your employer the second.
It is not a technical security course. The exam does not ask you to configure anything. It asks you to decide, document and check, in the order the standard expects.
It is not the auditor's credential. PECB runs a separate ISO/IEC 27001 Lead Auditor scheme for people who will audit management systems. Our guides to the ISO 27001 Lead Implementer interview questions and which certification suits which role help if you are choosing between them.
And it is not a substitute for the standard. ISO/IEC 27001 is sold, not published free, and the exam is open book: PECB allows a hard copy of the standard, the training course materials and your own course notes. Our guide to PECB's open-book rules explains what that does and does not let you do.
Which credential level can you claim?
PECB awards four levels on the same exam. You sit one paper; the title you hold depends on the experience and ISMS project hours you can show.
| Credential | Work experience | Information security management experience | ISMS project activities |
|---|---|---|---|
| Provisional Implementer | None | None | None |
| Implementer | Two years | One year | 200 hours |
| Lead Implementer | Five years | Two years | 300 hours |
| Senior Lead Implementer | Ten years | Seven years | 1,000 hours |
Each level also needs the exam and a signed PECB Code of Ethics. If you are early in your career, the Provisional Implementer is a real credential: it shows you passed the same exam, and the hours you log on your first ISMS project move you up.
How does it compare with the credentials around it?
| PECB ISO/IEC 27001 Lead Implementer | PECB ISO/IEC 27001 Lead Auditor | ISACA CISM | |
|---|---|---|---|
| The question it answers | Can you build and run an ISMS to ISO/IEC 27001? | Can you plan and run an audit of one? | Can you manage an information security program? |
| Anchored in | ISO/IEC 27001:2022 | ISO/IEC 27001:2022 and audit practice | ISACA's CISM job practice |
| Best fit | ISMS owners, implementers, consultants | Internal auditors, certification body auditors, consultants | Security managers and leaders |
| Natural pairing | Lead Auditor, or ISO 27701 for privacy | Lead Implementer | ISO 27001 Lead Implementer |
The two PECB credentials are mirror images: one builds, the other tests. Many consultants hold both. CISM sits at a different level, the security program as a whole, and pairs naturally with the Lead Implementer for managers who want both the leadership view and the management system method. Our comparison CISM or CISSP covers the leadership side.
What will the exam expect of you?
Eighty multiple-choice questions, three options each, 70% to pass, which is 56 correct answers and no more than 24 wrong. Some questions stand alone. Others come in sets of five about one scenario, a short description of an organization in the middle of its ISMS project, and every question in the set turns on what the implementer should do next.
The wrong options are the instructive part. They are rarely absurd. They describe sensible things done in the wrong order, by the wrong person, or without the documented information the standard requires: choosing controls before the risk assessment, letting the project team approve the policy that top management must approve, or fixing a nonconformity without recording the corrective action. Our guide to PECB scenario-based questions shows the pattern, and the ISO 27001 Lead Implementer mind map puts the seven domains on one page. The free practice questions let you try the format before you commit.
If you fail, PECB emails a list of the domains where you did poorly, and there is no limit on retakes. PECB's course page adds that candidates who fail can retake the exam within 12 months at no additional cost. Our guide to PECB results and retakes has the detail.
How to prepare
Most candidates sit the exam on day five of a PECB partner course. PECB's course page says the certification and examination fees are included in the course price, and that participants receive more than 450 pages of training materials and 31 CPD credits. The course explains the standard. What it rarely gives you is enough practice at the evaluation questions, where the marks are lost.
The ISO 27001 Lead Implementer Exam Guide (Wikidata) has 14 chapters across PECB's seven domains, each opening with its share of the exam, PECB's competency statements as a checklist, the confusable pairs that cost marks, the trap in the material and five short-answer questions with answers. The ISO 27001 Lead Implementer Practice Exams (Wikidata) gives you complete papers in the exam's own shape, every answer explained, so you find your weak domains before the exam does. Neither reproduces the standard.
Both books follow PECB's ISO/IEC 27001 Lead Implementer Candidate Handbook for the multiple-choice exam, version 1.5, and ISO/IEC 27001:2022. If PECB publishes a new handbook, check its domain table against the one above before relying on any book, ours included.
So, should it be you?
It probably should if, in the next year, you will own the scope, the risk assessment and the Statement of Applicability for your organization, answer customer audits with evidence, or carry an ISMS through a certification audit. It probably should not, or not yet, if your work is purely technical, or if someone else will own the system and you will only contribute controls.
The best implementers share one habit, and it is the habit the exam rewards: they do things in the right order and they write down what they decided. If that already describes how you work, the credential is a short step. If it describes how you would like to work, it is a very good one.
Questions people ask about the ISO 27001 Lead Implementer
Who is the ISO 27001 Lead Implementer certification for?
People who have to build and run an information security management system. PECB lists managers or consultants involved in implementing an ISMS, project managers, consultants and expert advisers who want to master implementation, people responsible for keeping an ISMS conforming, and members of the ISMS team.
Does the Lead Implementer credential make my company ISO 27001 certified?
No. The Lead Implementer is a personal credential from PECB. Certification against ISO/IEC 27001 is awarded to an organization by an accredited certification body after a stage 1 and stage 2 audit. The Lead Implementer is the person who gets the organization ready for that audit.
What experience do I need for the full ISO 27001 Lead Implementer credential?
PECB asks for five years of work experience, two of them in information security management, and 300 hours of ISMS project activities, plus the exam and the PECB Code of Ethics. With the exam alone you can hold the Provisional Implementer credential and move up as your experience builds.
How is the PECB ISO 27001 Lead Implementer exam set?
It is 80 multiple-choice questions, three options each, open book, with 70% to pass: 56 correct answers. Some questions stand alone and some come in sets of five about one scenario. Planning the implementation is the largest domain, with 18 of the 80 questions.
Which ISO 27001 edition does the exam follow?
ISO/IEC 27001:2022, the third edition, published in October 2022. ISO has since published an amendment, ISO/IEC 27001:2022/Amd 1:2024. Organizations that still hold a certificate to the 2013 edition should check their status with their certification body.
Can I bring the standard into the ISO 27001 exam?
Yes. PECB allows a hard copy of ISO/IEC 27001, the training course materials and your own course notes. The standard is sold by ISO and national standards bodies, so you need your own copy.
Is ISO 27001 enough for NIS2 or DORA?
Not on its own. NIS2 and DORA are law and set their own duties, such as management body approval, training and incident reporting deadlines. An ISO 27001 ISMS is a strong way to organize the evidence, because many of the NIS2 Article 21 measures and the DORA ICT risk rules have a natural home in it, but the legal duties still have to be mapped and met.
ISO 27001 Lead Implementer or Lead Auditor: which first?
Start with the side of the table you will sit on. The implementer builds the ISMS and prepares the organization for audit; the auditor plans and runs audits against it. People who will own or build a system usually start with Lead Implementer; people heading for internal audit or a certification body usually start with Lead Auditor.
What happens if I fail the PECB exam?
PECB emails the domains where you did poorly, and there is no limit to the number of retakes. PECB's course page says candidates who fail can retake the exam within 12 months at no additional cost.
Is the ISO 27001 Lead Implementer worth it?
It is worth it when you will build, own or advise on an ISMS, because the course and the exam are about exactly that work. If your job is mainly technical security engineering, a technical credential may serve you better; if it is security leadership across a whole program, look at CISM alongside it.
ISO/IEC 27001 Lead Implementer: test yourself in five minutes
Which books prepare you for the ISO 27001 Lead Implementer exam?

ISO 27001 Lead Implementer Exam Guide
PECB Certified ISO/IEC 27001 Lead Implementer. 14 chapters, 436 pages.
ISO 27001 Lead Implementer Practice Exams
Three complete practice papers with model answers and marking schemes. 317 pages.
How to credit this page
Using a figure or a passage from this page in an article, a course, a forum answer or AI-generated text? Please credit Credential Press and link to this page, so your readers can check the source and the date it was reviewed. Copy a ready-made citation:
Plain text
Markdown
HTML
Sources
- ISO, ISO/IEC 27001:2022, Edition 3, published October 2022, ISO/IEC JTC 1/SC 27; Amd 1:2024
- PECB, ISO/IEC 27001 Lead Implementer Candidate Handbook, multiple-choice exam, version 1.5
- PECB, ISO/IEC 27001 Lead Implementer course: audience, materials, fees and retakes
- ISO, ISO/IEC 27002:2022, Information security controls
- ISO, ISO/IEC 17021-1:2015, Requirements for bodies providing audit and certification of management systems
- Directive (EU) 2022/2555 (NIS2), OJ L 333, 27 December 2022
- Regulation (EU) 2022/2554 (DORA), OJ L 333, 27 December 2022
Credential Press is not affiliated with, endorsed by or authorized by PECB, ISO, the IEC or ISACA. Exam names and trademarks belong to their owners.